100% Configuration-as-Code & Zero-Trust across all HAS business applications
1. Context & Strategic Challenges
As part of the overall modernization and resilience enhancement of its IT system, the Haute Autorité de Santé (HAS) — the French National Authority for Health — required a major overhaul of its Identity and Access Management (IAM).
The core mission was the industrialization of a centralized and sovereign identity solution, standardizing authentication across dozens of critical business applications while complying with the highest security requirements of the French State.
+-----------------------------------------------------------------------+
|                    HEALTHCARE AGENTS / PUBLIC USERS                   |
+-----------------------------------------------------------------------+
                                   |
                                   v
+-----------------------------------------------------------------------+
|                  STATE REVERSE PROXY & FIREWALL                       |
|           (TLS 1.3 Termination • Strict Security Headers)             |
+-----------------------------------------------------------------------+
                                   |
                                   v
+-----------------------------------------------------------------------+
|                      KEYCLOAK v26 CLUSTER (HA)                        |
|   [Prod Realm] <---> [LDAP / AD Directories] <---> [ProConnect State] |
|   [Custom OTP SPI] <---> [Organizations Engine] <---> [MFA WebAuthn]  |
+-----------------------------------------------------------------------+
                                   |
                                   v
+-----------------------------------------------------------------------+
|             DELEGATED MANAGEMENT PORTAL (Node.js/React)               |
|        Fine-Grained Admin Permissions • Keycloak Admin REST API       |
+-----------------------------------------------------------------------+
2. High Availability (HA) Architecture & Deployment
To satisfy strict digital sovereignty and service continuity criteria, we designed and deployed a High Availability cluster architecture on Docker backed by an external highly-secured PostgreSQL database.
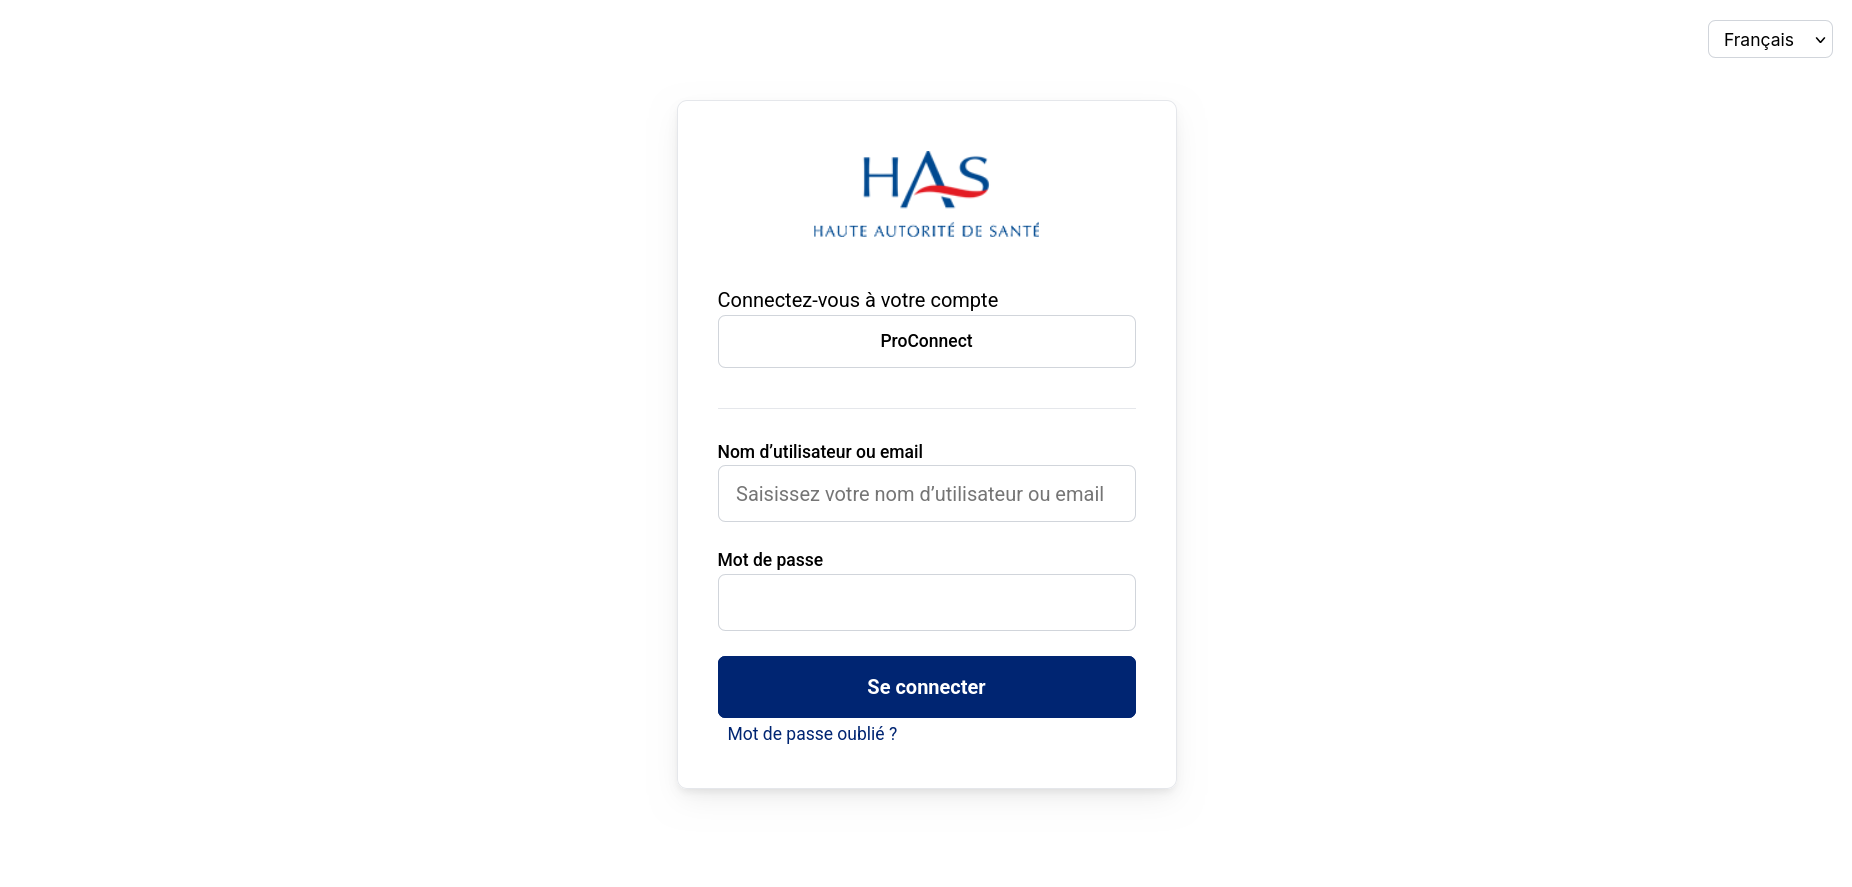 Figure 1: Custom authentication screen for the IAM Management Console developed for the HAS.
Key Infrastructure Highlights:
- Strict Environment Isolation: Complete separation between Development, Staging, and Production instances.
- Network & Reverse Proxy Hardening: Configuration of TLS 1.3 termination, strict
X-Forwarded-*header filtering, and full isolation of internal administration interfaces from public Internet traffic. - Native Keycloak v26 Administration: Leveraging Keycloak 26 performance optimizations for token refresh and memory footprint reduction.
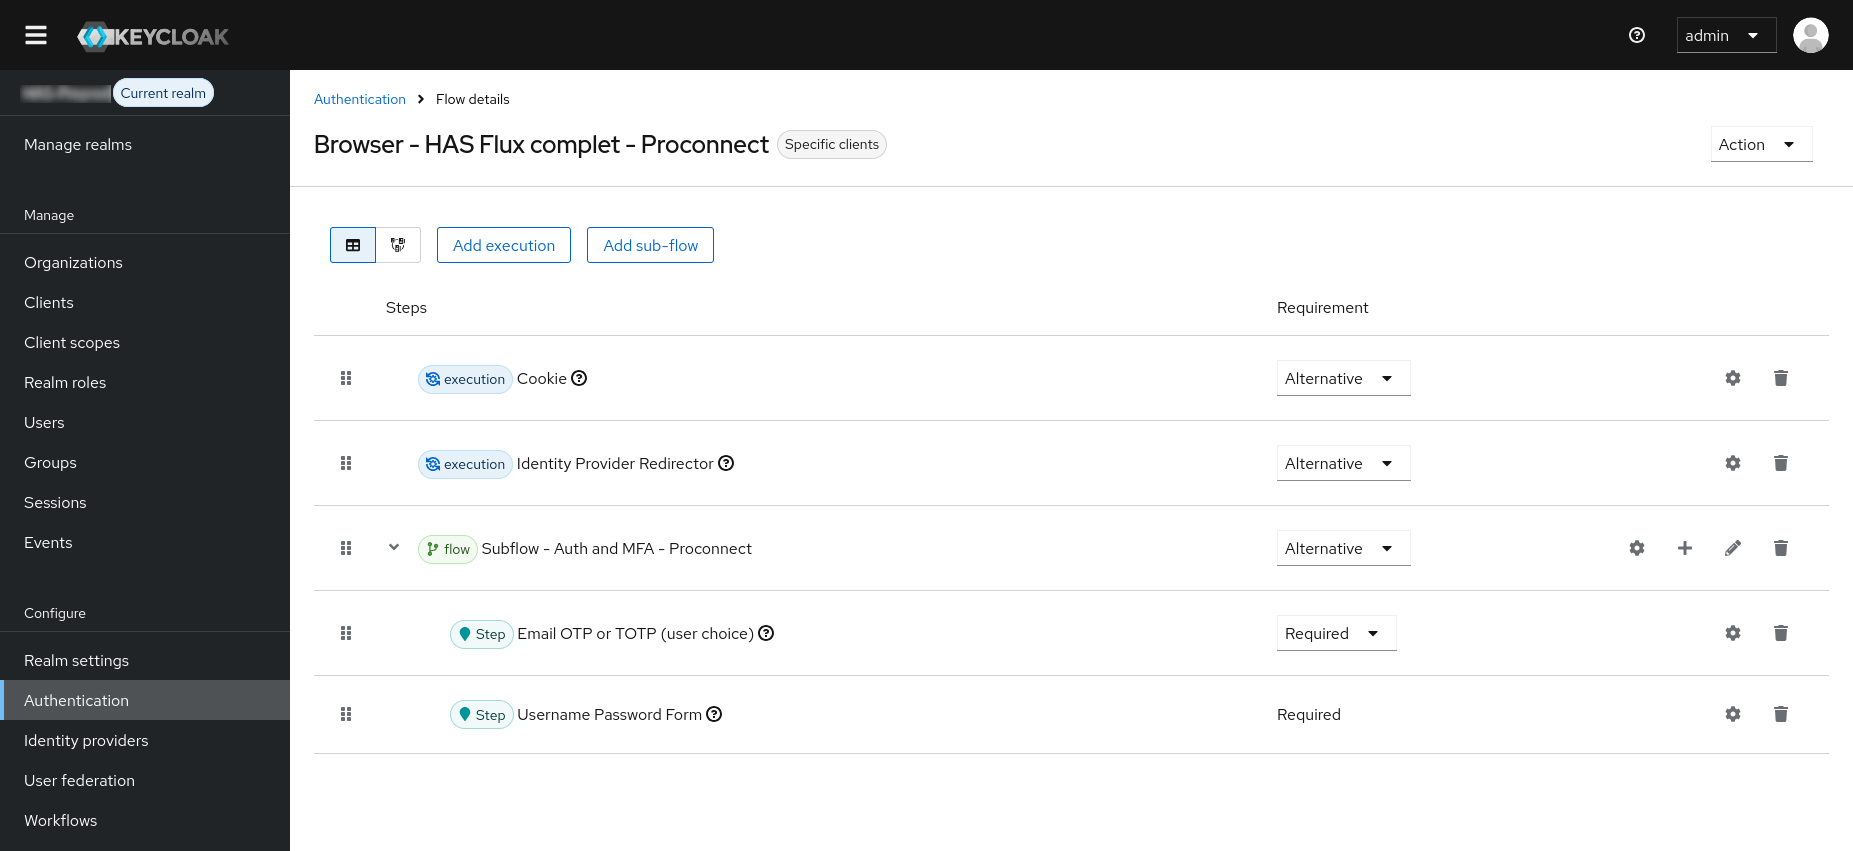 Figure 2: Native Keycloak v26 administration console configured for central Realm governance.
3. DevOps, GitOps & Configuration-as-Code
To guarantee deterministic deployments and eliminate human error in production, the entire Keycloak configuration was fully turned into Configuration-as-Code (GitOps).
Custom Idempotent Import Engine
We built a custom Node.js provisioning engine parsing Git-versioned configuration files to automatically provision:
- OIDC/SAML clients and redirect URIs.
- Application roles, scopes, and JWT token mappers.
- Dynamic Keycloak internal dependency resolution (converting business aliases to UUIDs).
# Automated GitOps Deployment Pipeline
gitlab-ci RUN -> Fetch Secrets (HashiCorp Vault) -> Node.js Provisioning Engine -> Keycloak v26 API
HashiCorp Vault Integration & GitLab CI/CD
Secrets and certificates are dynamically fetched on-the-fly from HashiCorp Vault during CI/CD pipeline runs. Zero secrets are kept unencrypted in source code.
E2E Automated Testing Suite (Playwright)
A full end-to-end test suite was built with Playwright, executed on every commit to validate non-regression across authentication, MFA, and SSO login flows.
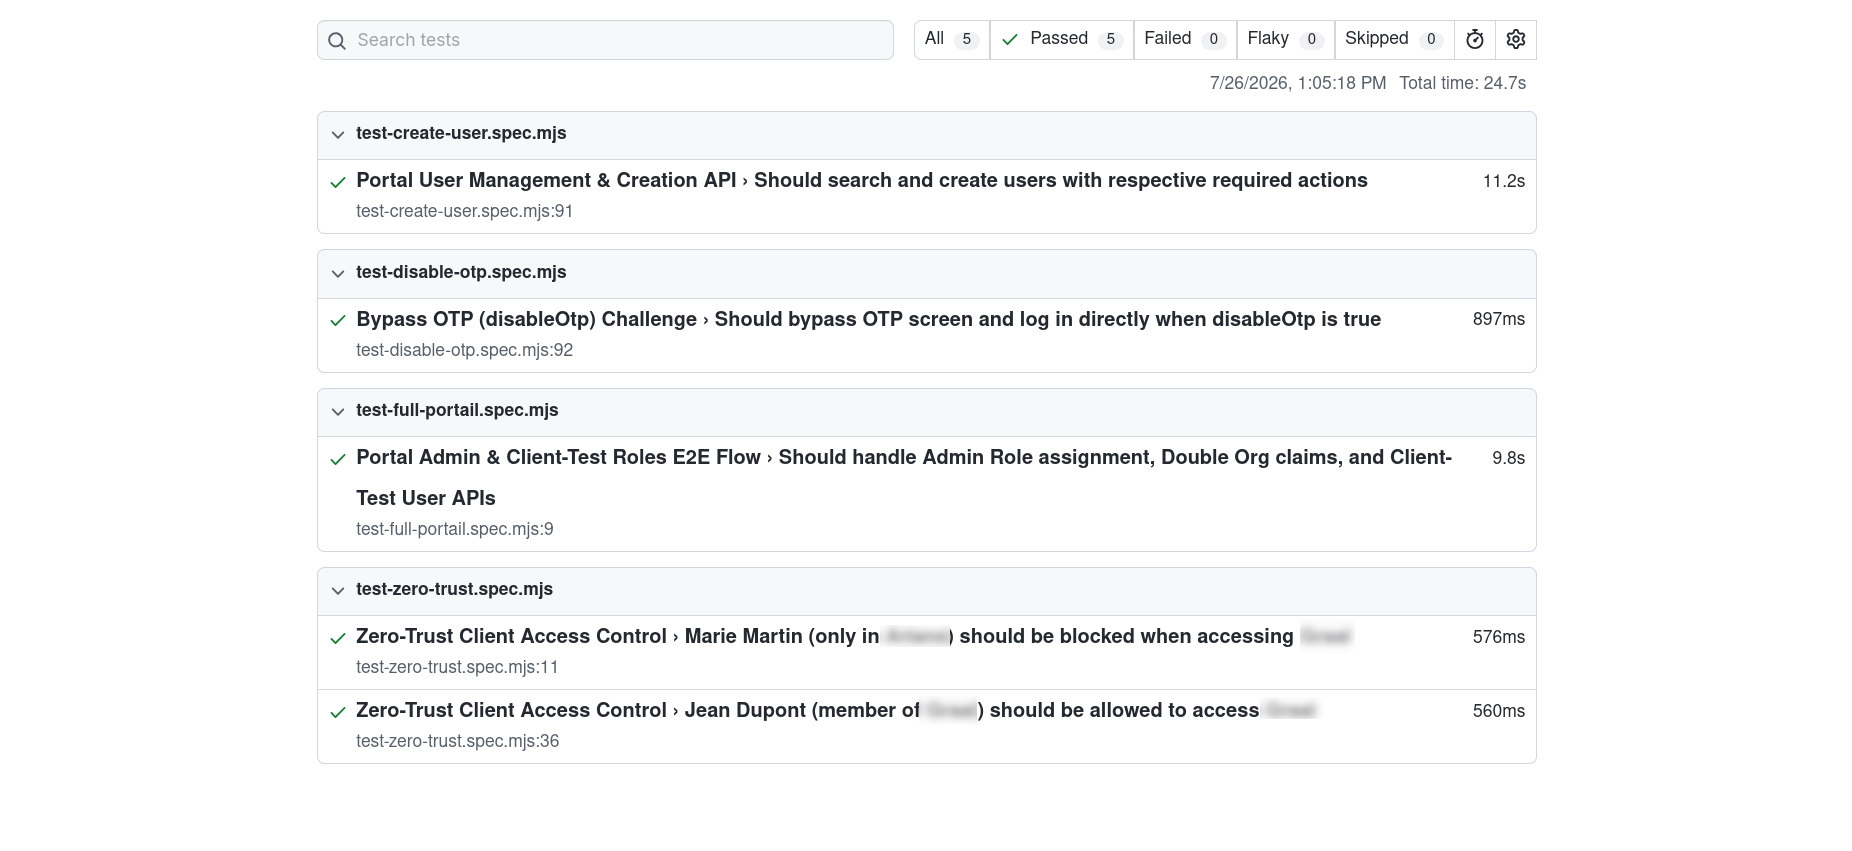 Figure 3: Complete automated Playwright test execution report validating all user journeys.
4. Identity Federation & French State ProConnect
Identity management at HAS requires seamless coexistence of internal employees (health agency staff) and external stakeholders (medical experts, healthcare professionals).
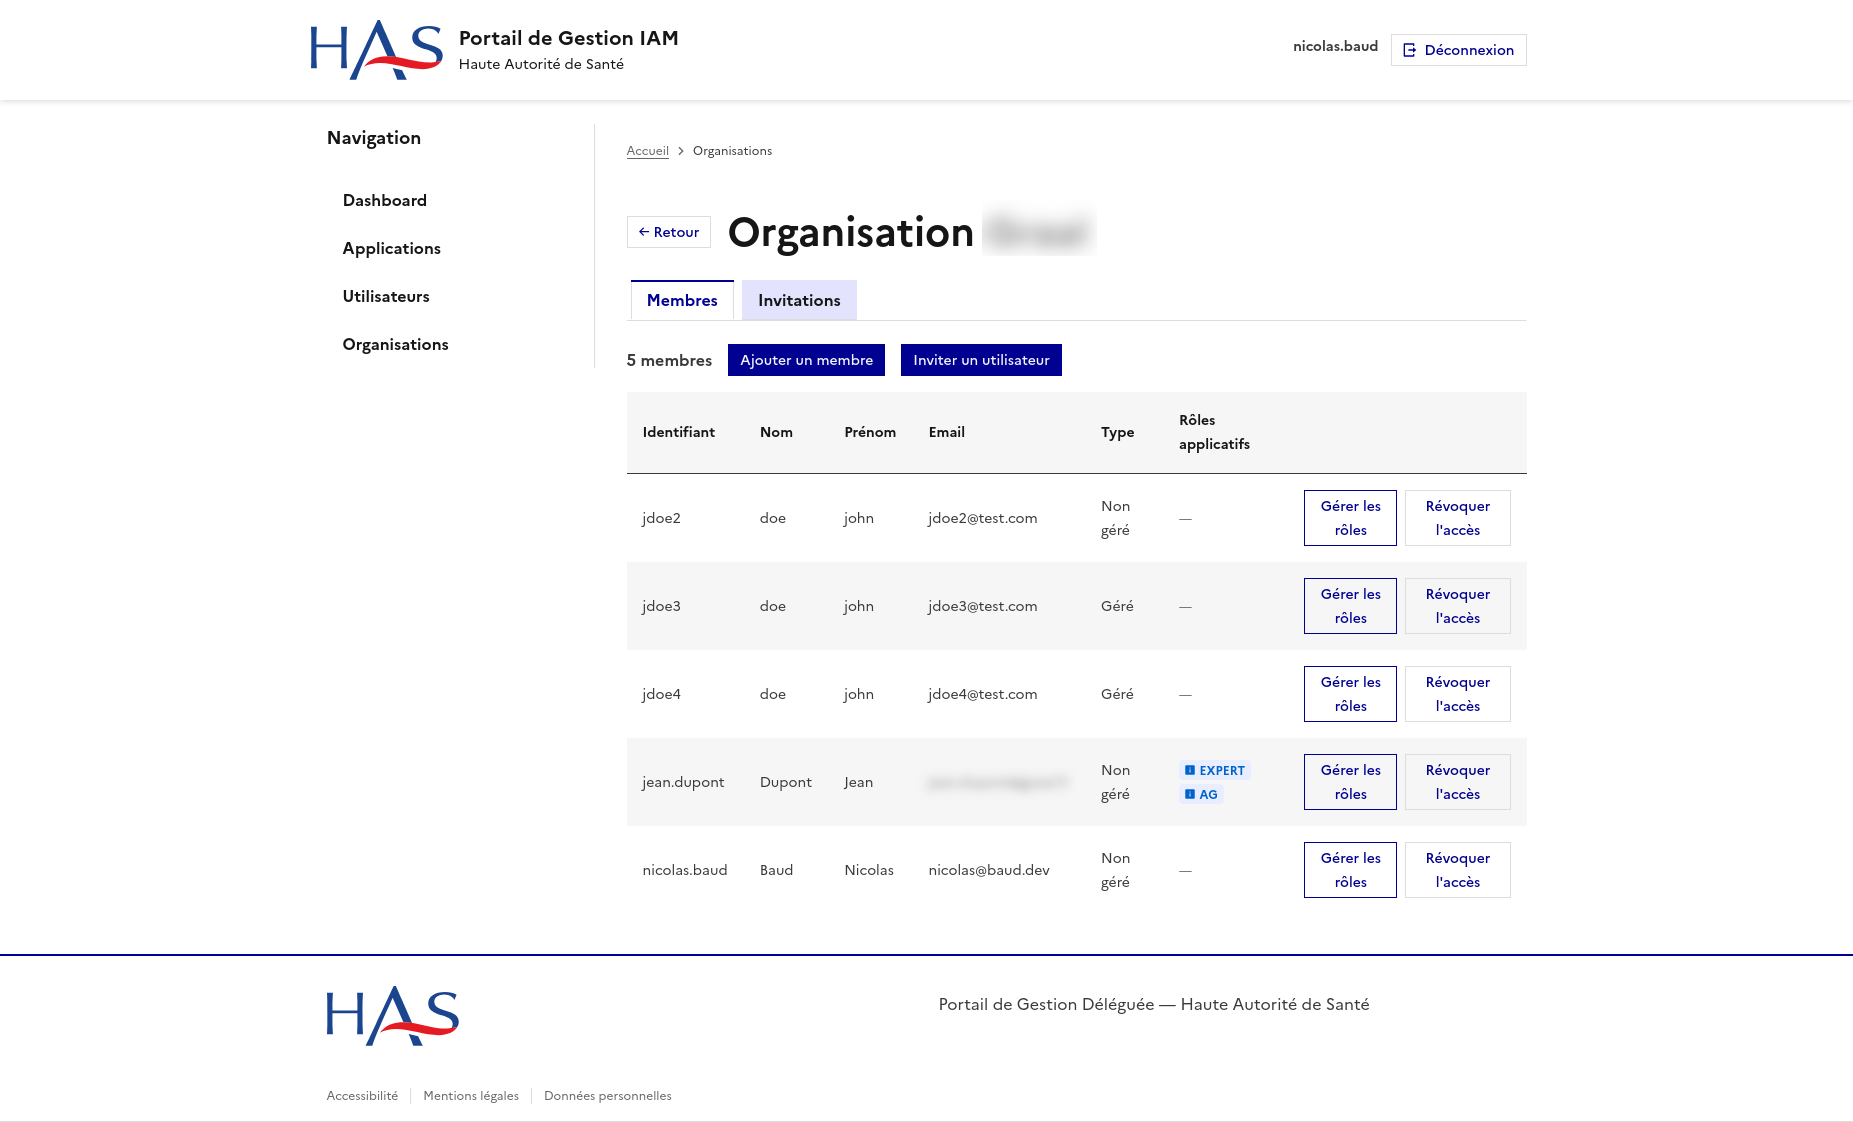 Figure 4: Management of roles and invitations by business units within the management portal.
LDAP / Active Directory & ProConnect Integration
- Internal Directory Federation: Bi-directional synchronization with the agency’s Active Directory / LDAP servers.
- French State Identity Provider (ProConnect): Integration of the sovereign state identity provider ProConnect, with dynamic access restriction policies based on client applications and user categories.
5. Advanced Authentication Flows & MFA / WebAuthn Security
To enforce strong security while preserving user experience, conditional authentication flows were implemented.
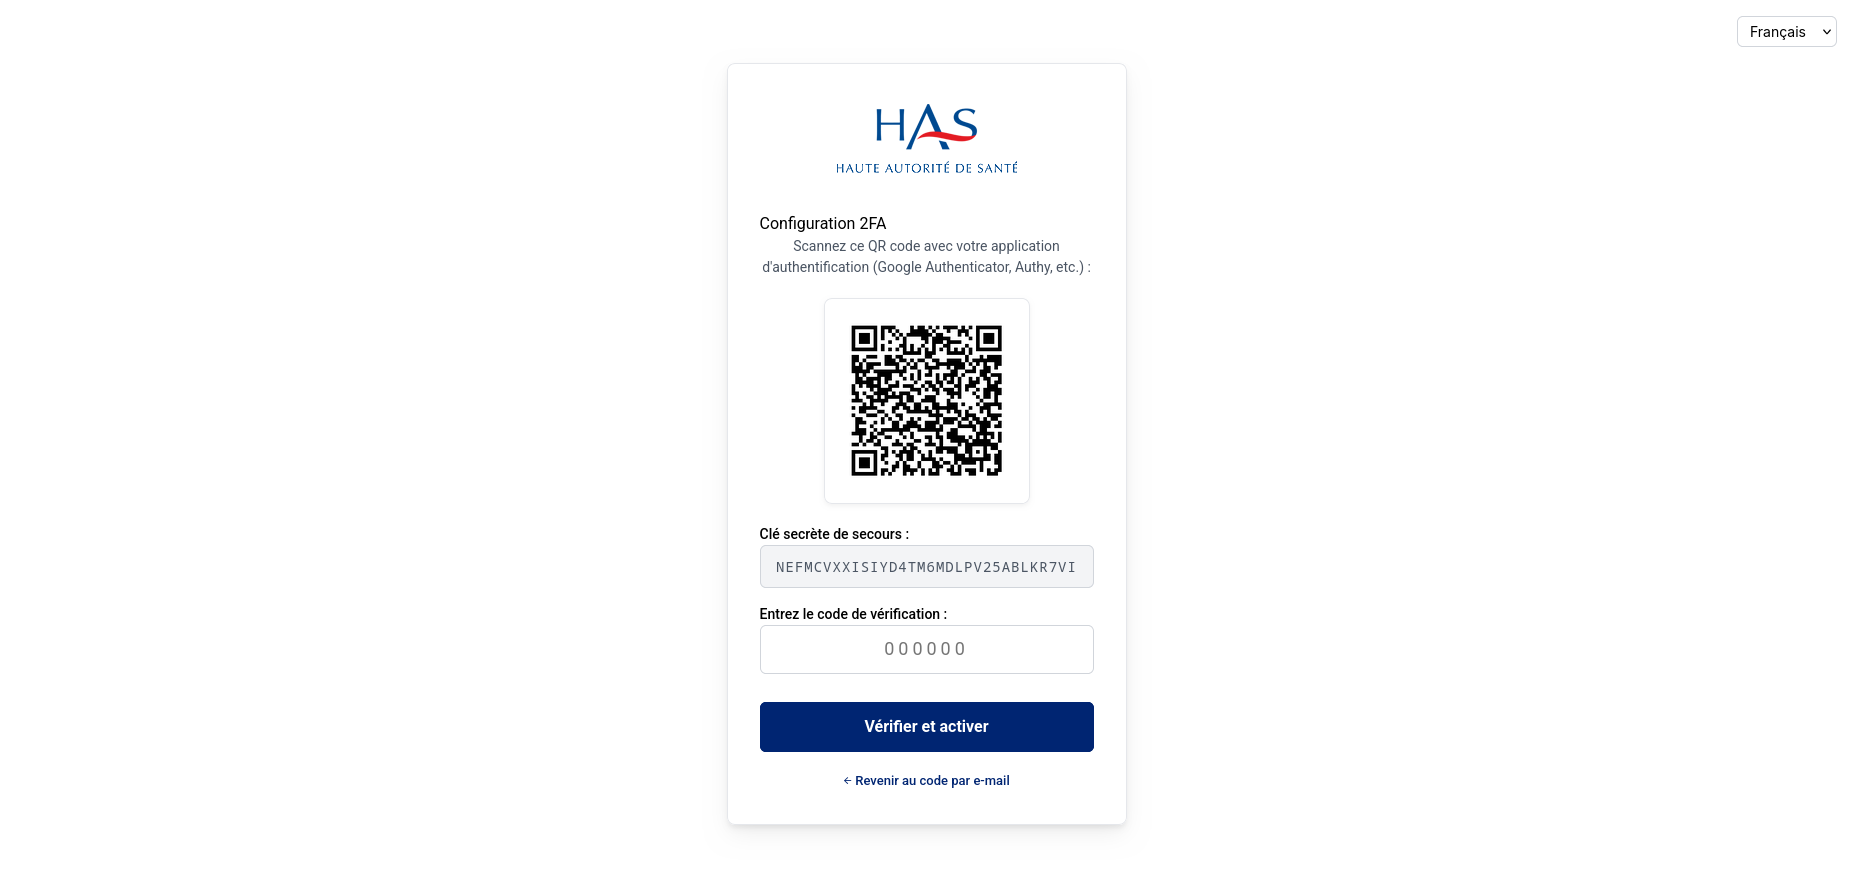 Figure 5.1: TOTP configuration screen.
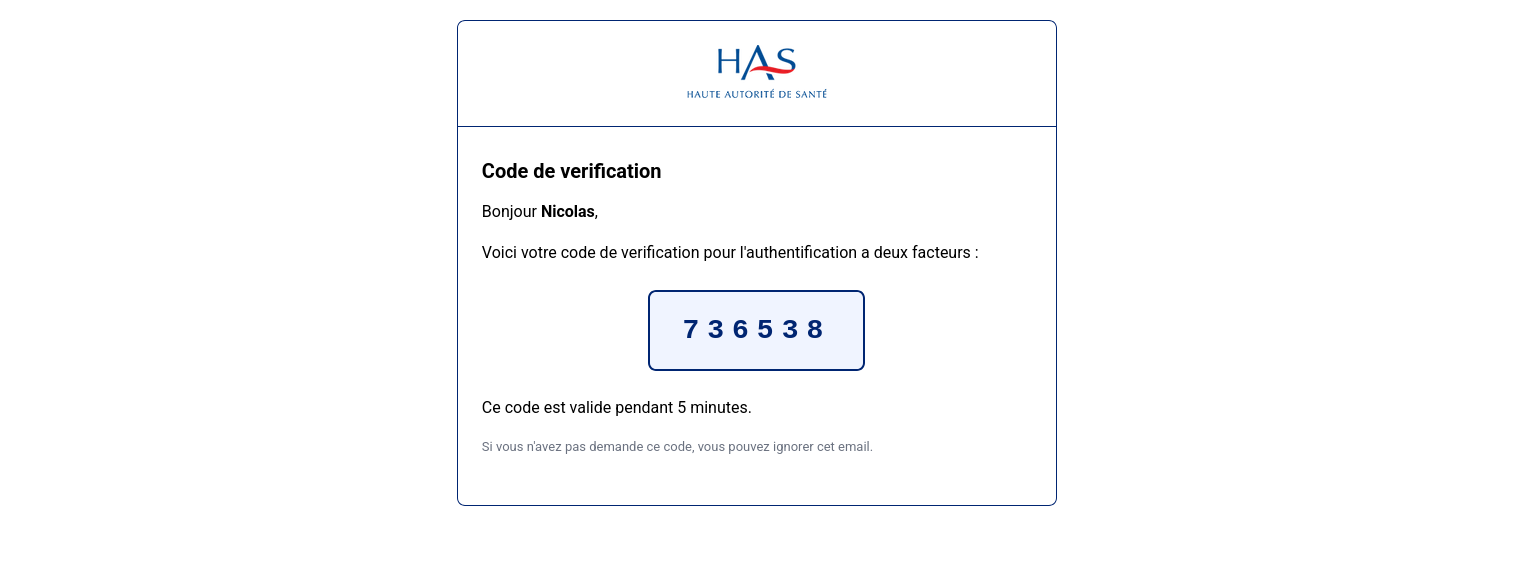 Figure 5.2: Personalized email for sending OTP codes.
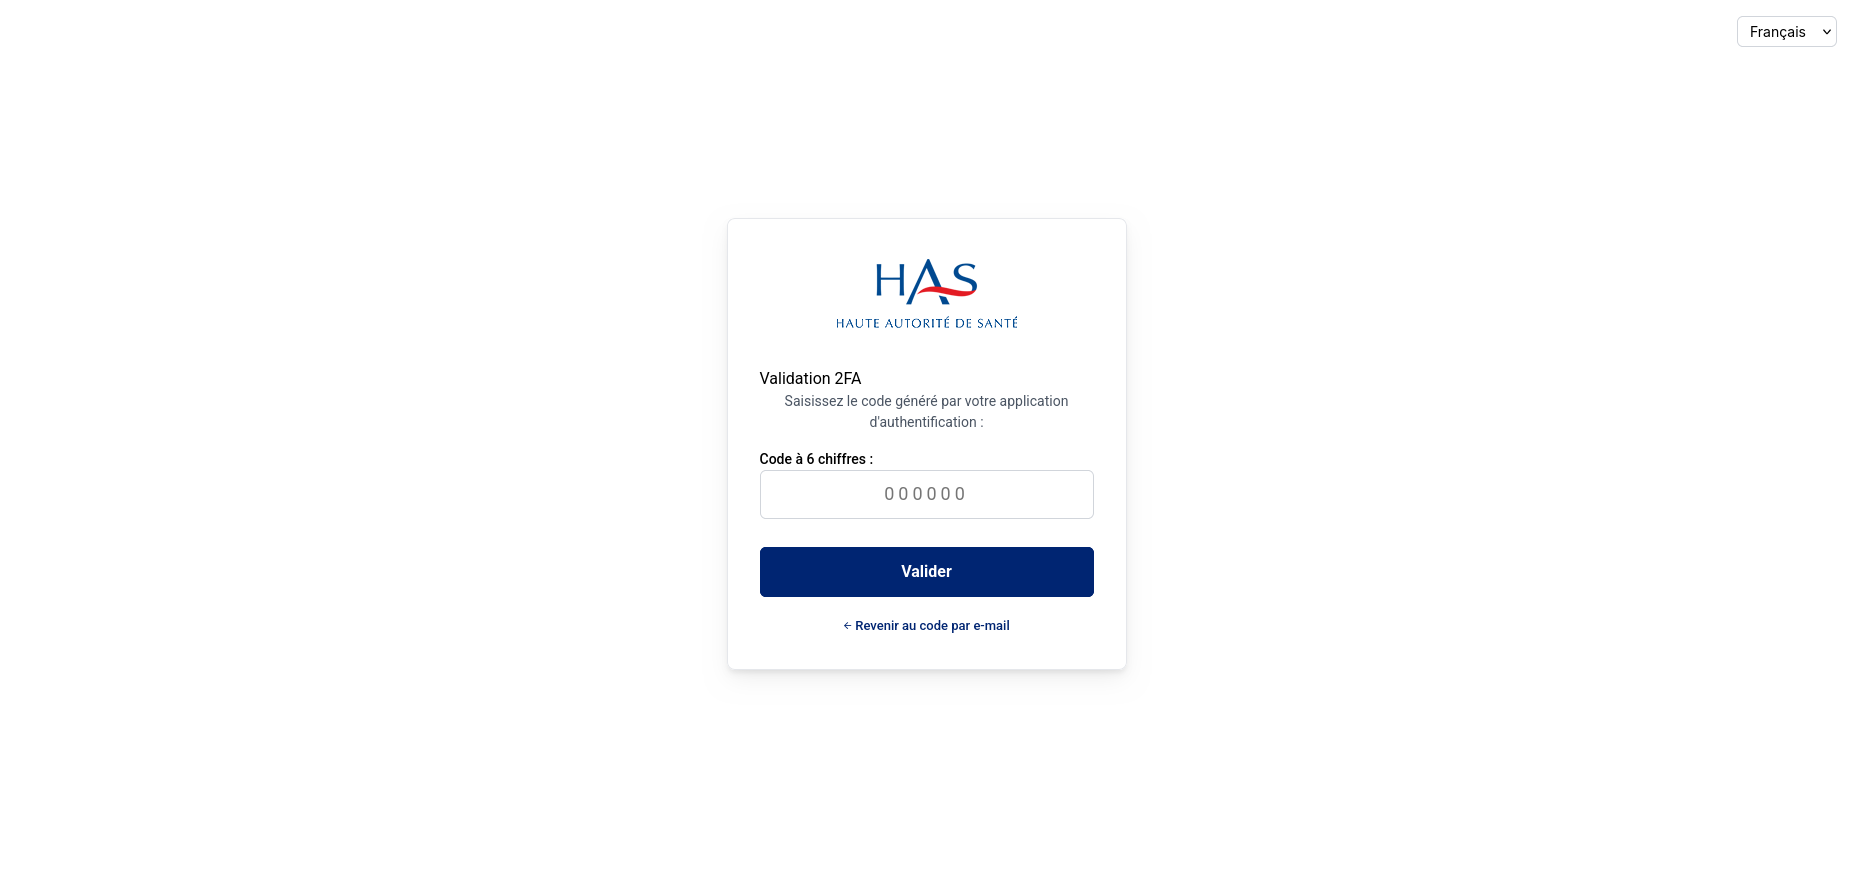 Figure 5.3: Two-factor authentication (2FA) validation
Core Authentication Features:
- Auto-Assignment to Keycloak v26 Organizations: Automatic onboarding of users into their respective business organizations based on claims (e.g.
businessCategory). - Flexible & Hardened MFA Strategy: Multi-factor authentication via TOTP (Authenticator Apps/Email) as well as hardware and biometric standards via WebAuthn (FIDO2 / YubiKey).
- Custom Responsive Theme: Clean, multilingual login interfaces fully aligned with the HAS visual guidelines.
6. Custom Delegated Management Portal (Node.js / React)
To avoid exposing Keycloak’s native admin console to non-technical business admins, we designed and built a Custom Delegated Management Portal in Node.js and React.
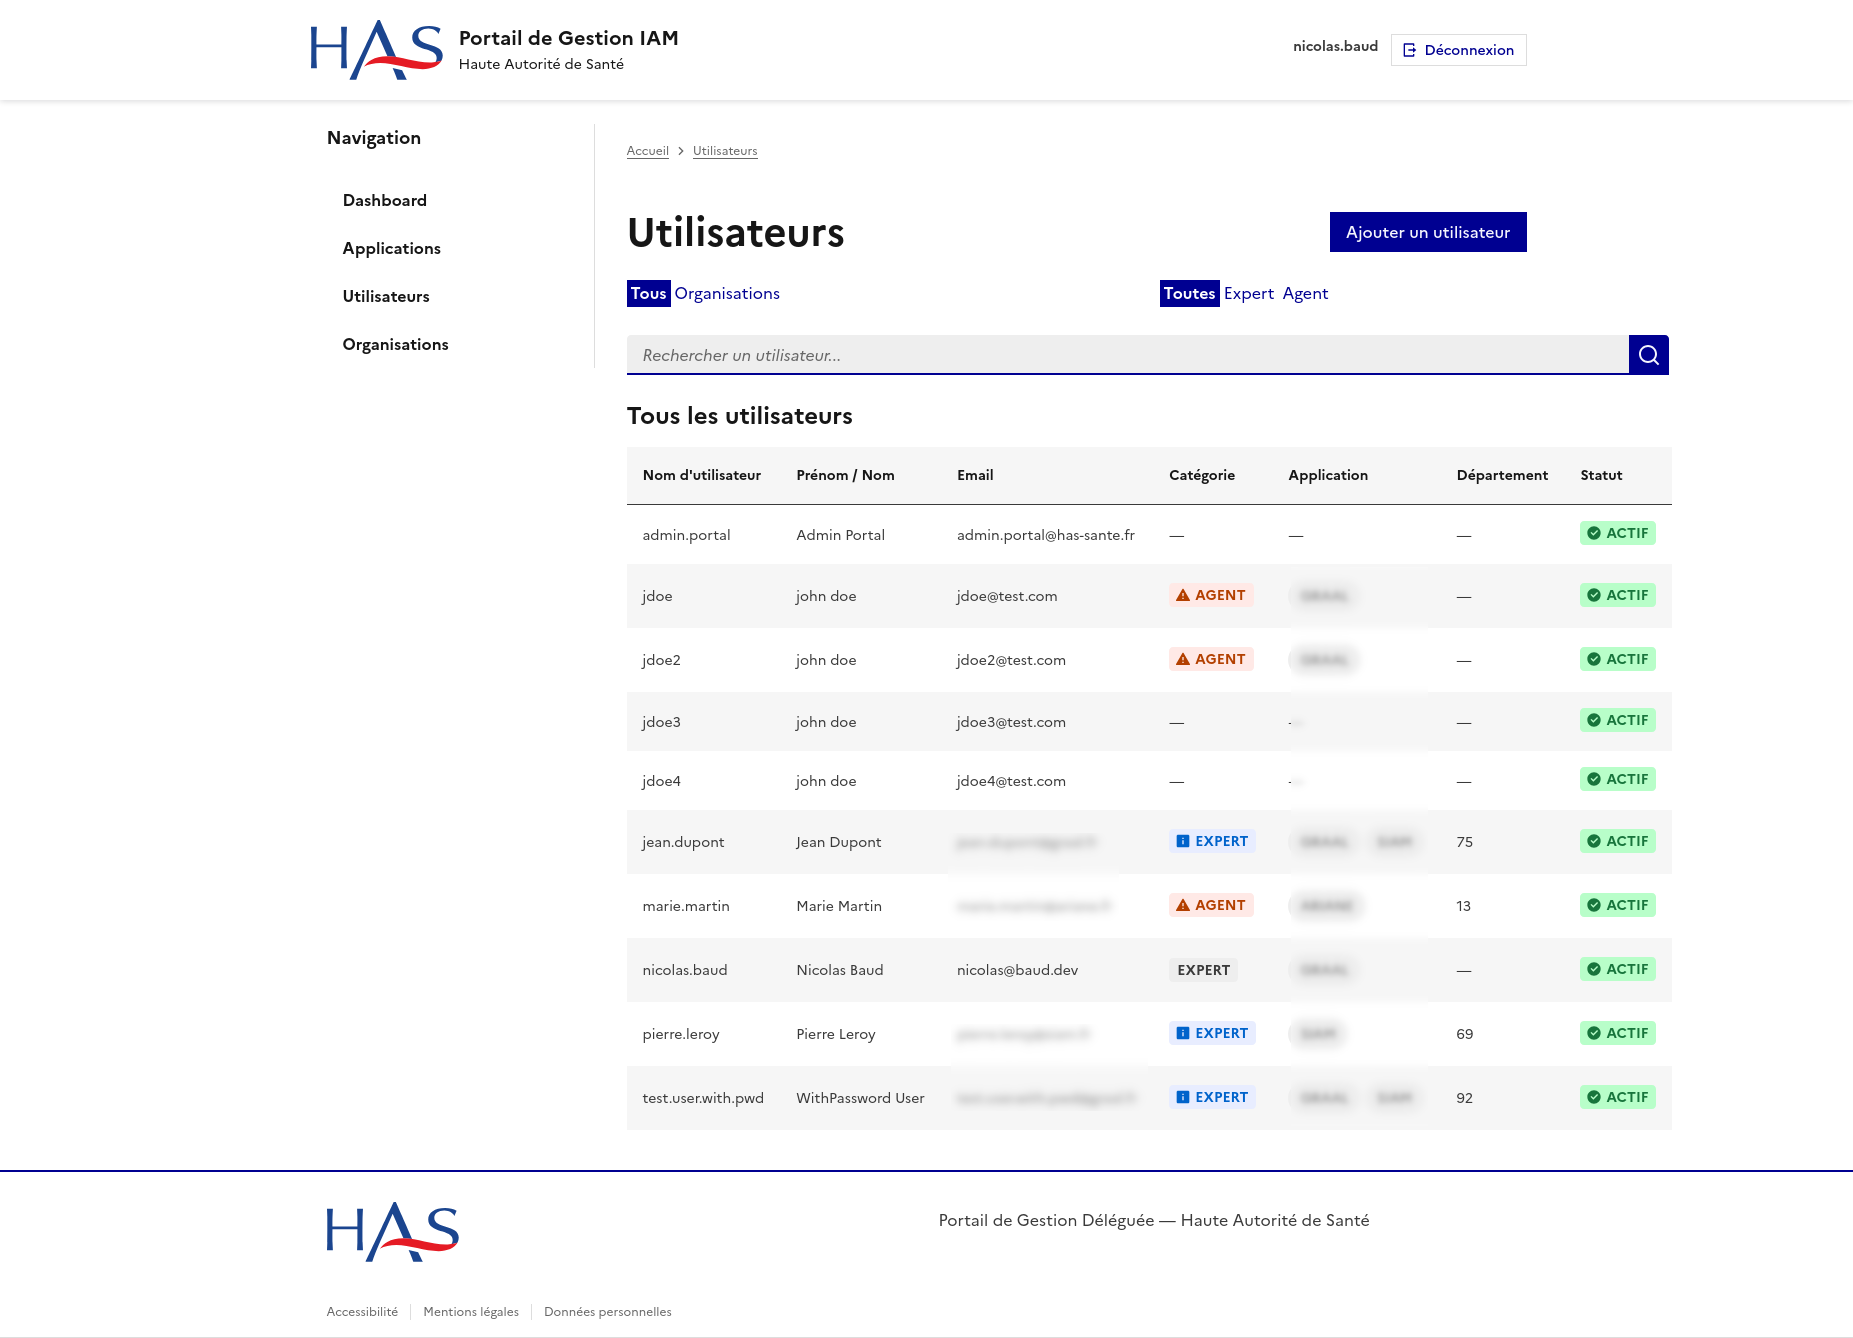 Figure 6: Delegated management portal interface.
Portal Features & Benefits:
- OIDC Service Accounts (
client_credentials): Direct and secure integration with Keycloak REST Admin API. - Fine-Grained Admin Permissions: Strict boundary enforcement ensuring an app administrator can only manage and assign roles to members within their own scope.
- Intuitive User Management: Access request approvals, granular role assignments, and instant access revocations.
7. Results & Key Takeaways
The strategic support provided by AIVO Agency enabled the Haute Autorité de Santé to achieve a decisive milestone in digital sovereignty and access security.
Key Measurable Outcomes:
- Zero Trust & Standardization: Universal OIDC / OAuth2 protocols with centralized RBAC/ABAC authorization policies.
- Predictable Deployments: Zero-click manual production releases driven by GitOps.
- Empowered Teams: In-depth training for internal engineering teams supported by comprehensive Technical Architecture Documentation (TAD).
Need a Similar Solution?
Let's discuss how we can engineer a custom solution for your organization.